Asha Javeed
Contributing Writer
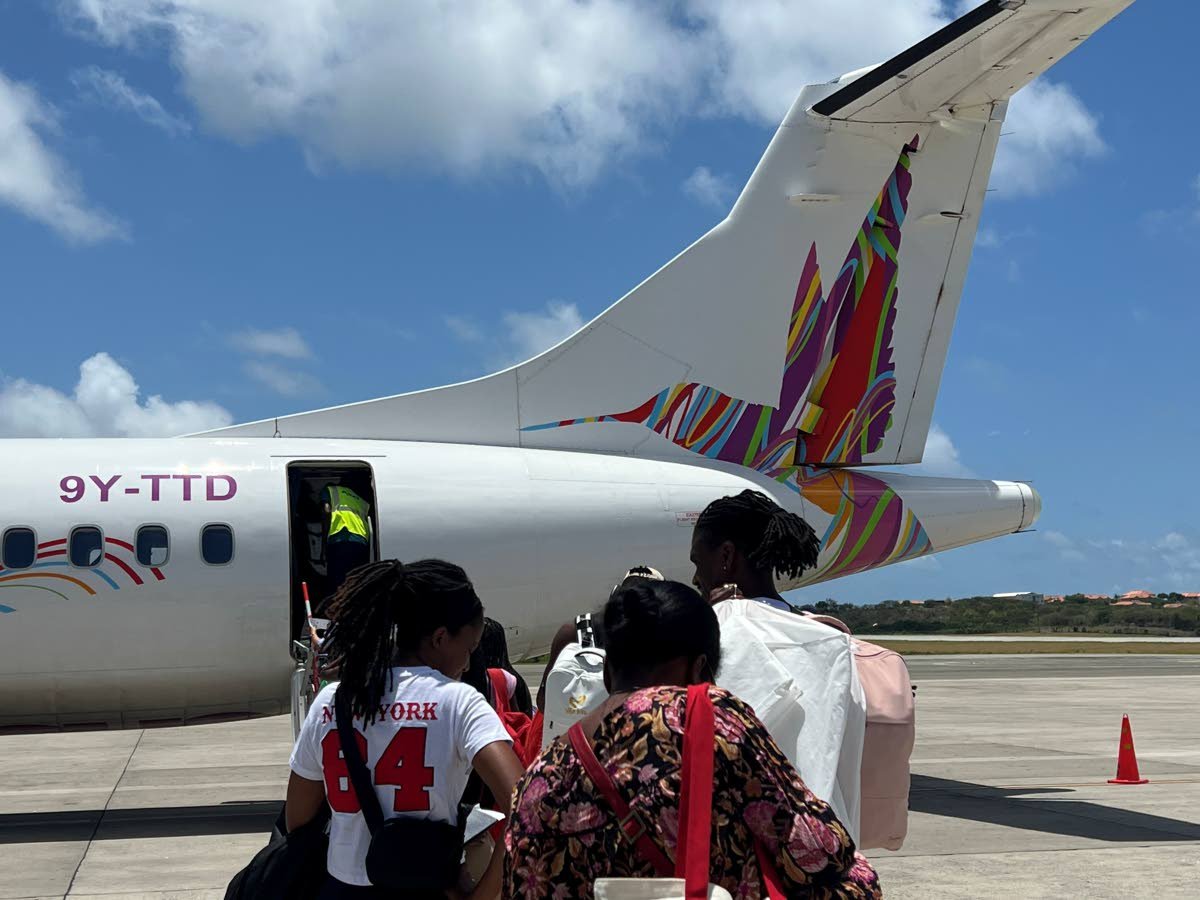
A data breach within one of Caribbean Airlines’ (CAL) third-party technology service providers has exposed the data of some of its customers.
According to an email sent to affected CAL passengers yesterday, the breach of CAL’s reservation and booking systems happened on November 5.
“On 5 November 2026, Caribbean Airlines was informed that an unauthorised party gained access to certain reservation information through a compromised system account. Based on the information currently available, your reservation record may have been affected. Both Caribbean Airlines and the third-party service provider are actively investigating the incident. The investigation is ongoing, and we do not yet have all their information necessary to confirm the precise data elements associated with your reservation that may have been accessed,” the email said.
While CAL did not identify the company that handles its reservation and booking system in its email, Guardian Media has learnt that it is managed by the international firm, Amadeus.
The email said the information potentially affected “may include reservation-related details such as your name, booking reference, travel itinerary, contact information, and other information contained in your booking record. Not every reservation record contains the same information.”
CAL has not made the breach public except to identified customers. Guardian Media was told that the company had a legal requirement to do so because of data protection laws in the various jurisdictions in which it operates.
A company official yesterday confirmed the breach did occur but declined to give more information because of the investigation. The official told Guardian Media that CAL is reaching out to affected passengers only and noted that no payment card data was exposed. There was also no word on how many customers were affected.
“At this time, we are not aware of any evidence that your information has been misused. However, as a precaution, we recommend that you remain alert for unexpected emails, messages, or phone calls that reference your travel or booking information and avoid sharing personal information unless you are satisfied that the request is legitimate,” the email said.
CAL’s email said that Amadeus has taken immediate steps to contain the incident, including resetting the compromised credentials, enhancing access controls, and implementing additional monitoring measures.
“We will provide you with further information as it becomes available, including updates on the investigation (and) any additional steps being taken by Caribbean Airlines or the third-party service provider. We sincerely regret any concern this incident may cause. Caribbean Airlines takes the protection of personal information seriously and remains committed to safeguarding your personal data through appropriate security and privacy measures,” it said.
CAL is the latest airline to be affected by the Amadeus breach. According to international media reports, multiple airlines that use Amadeus have reported unauthorised access to passenger data in systems with exposed information, in some cases, including passport numbers and contact details.
Some of the affected airlines that have acknowledged an Amadeus breach are Scandinavian Airlines, Japan Airlines, Thai Airways, and Cathay Pacific
According to international reports, the access occurred between August 2023 and September 2026, and Amadeus notified carriers of the breach between October 20 and October 28, based on dates provided by multiple airlines. A statement by Amadeus on October 30 said there was a vulnerability affecting its travel booking display environment that made certain booking data accessible, but there is no evidence that payment or financial data was accessed.
Other airlines have identified how many of their customers were affected: Japan Airlines said approximately 92,000 customers of Japan Airlines and Japan Transocean Air were affected, including about 2,000 whose exposed information included additional personal details such as passport numbers, while Cathay Pacific said approximately 53,000 bookings were affected.
Locally, the most significant data breach occurred on October 9, 2023, at TSTT but was only made public on October 27, after Falcon Feeds, an India-based technology security company, reported on its X social media account. It claimed to have access to 6GB of organisation data. On October 28, TSTT said in a statement that there was no compromise of customer data. On November 3, TSTT admitted that 6GB, or less than one per cent of the petabytes of the company’s data—1.2 million entries—was accessed, but that the majority of its customers’ data was not acquired and no passwords were compromised.
CAL Board
condemns Imbert
Meanwhile, the Caribbean Airlines (CAL) board yesterday took issue with statements made by former Finance Minister Colm Imbert.
In a statement yesterday, the board said it never sought a $1 billion bailout from the Government or that its former acting chief executive Nirmala Ramai had left the organisation.
CAL said Ramai is still the company’s Chief Operations Officer and continues to serve as a senior member of the airline’s Leadership Team.
“The Board firmly rejects the former minister’s criticism of its stewardship, which stands in direct contrast to the record of governance under the tenure of the previous Board. During that period, the previous Board of Directors of Caribbean Airlines was reprimanded for failing to follow the appropriate procurement requirements in the acquisition of several services. In fact, the former minister himself wrote to the then Chairman on December 23, 2024, identifying instances of non-compliance with the Public Procurement and Disposal of Property Act, 2015,” it said.
“Manpower reports also showed that the previous Board appointed persons to positions within the organisation without adherence to an appropriate recruitment process and without regard to the approved organisational chart. Further, the backlog of nine years of unaudited financials cannot be overlooked; contrary to prudent governance, these unaudited financials were used to award bonuses to a Senior Executive at that time, it said.
The board said the burden of cleaning up these irregularities, which speak to overall poor governance, now rests with the current Board and Management.