
The cyber attack against the Andorran Social Security Fund (CASS) has led to the opening of one internal investigation, parallel to the policeto clarify how the incident occurred. While the inquiries continue, the parapublic has already entered changes to the portal used by companies to register and terminate workers. One of the modifications, applied following the attack, prevents the identity of the person who is joining from being checked immediately.
Until now, when a company introduced the administrative identification number (NIA) and the start or end date of the employment relationship, the system displayed the name and surname of the insured. Since Wednesday, this data appears hidden with symbols. This complicates the error detection when entering the NIA and may cause a registration, cancellation or quote to be processed in the name of another person. Grandvalira Resorts explained that an error cannot be detected after registration: it is necessary to consult the list of insured persons on the portal afterwards, which generates more work with a current system that is inefficient. The company pointed out that, with the high volume of daily discharges during this period, they are applying measures to avoid these mistakes while waiting for solutions.
The change does not affect the same procedure as the cybercriminals were exploited to obtain names, surnames, sex, date and place of birth linked to 477,000 NIAhowever also limits visible personal information by entering this identifier. The CASS he admitted that the number of inquiries from citizens and businesses has increased related to the incident, despite ensuring that there has been no collapse of the service channels or of its website. As he explained, some declarants may have suffered temporary access blocks during the monitoring tasks, which have been resolved as soon as it has been recorded.
The parapublic affirmed that it continues to serve both the questions arising from the cyberattack as usual managementand that he cannot specify whether he will introduce new changes to the portals. On the other hand, theCybersecurity Agency has noted that the stolen data they do not, on their own, allow access to bank accounts or e-mails. The CASS has also ensured that no fraudulent intrusions have been detected in health information or related to the benefits of the holders of the GIRL affected
Rossell, yesterday at the Council.
SOCIAL SECURITY WILL HAVE TO DECIDE THE MEASURES
Rossell recalled that the incident affected digital certificates linked to four home computers, without accessing their internal systems. Among the exposed data are administrative identification numbers (NIA)names and dates of birth and an audit will have to clarify how the attack occurred and what fixes need to be applied. In the meantime, the case is being prosecuted and the CASS will appear at his own request before the General Councilas the minister pointed out.
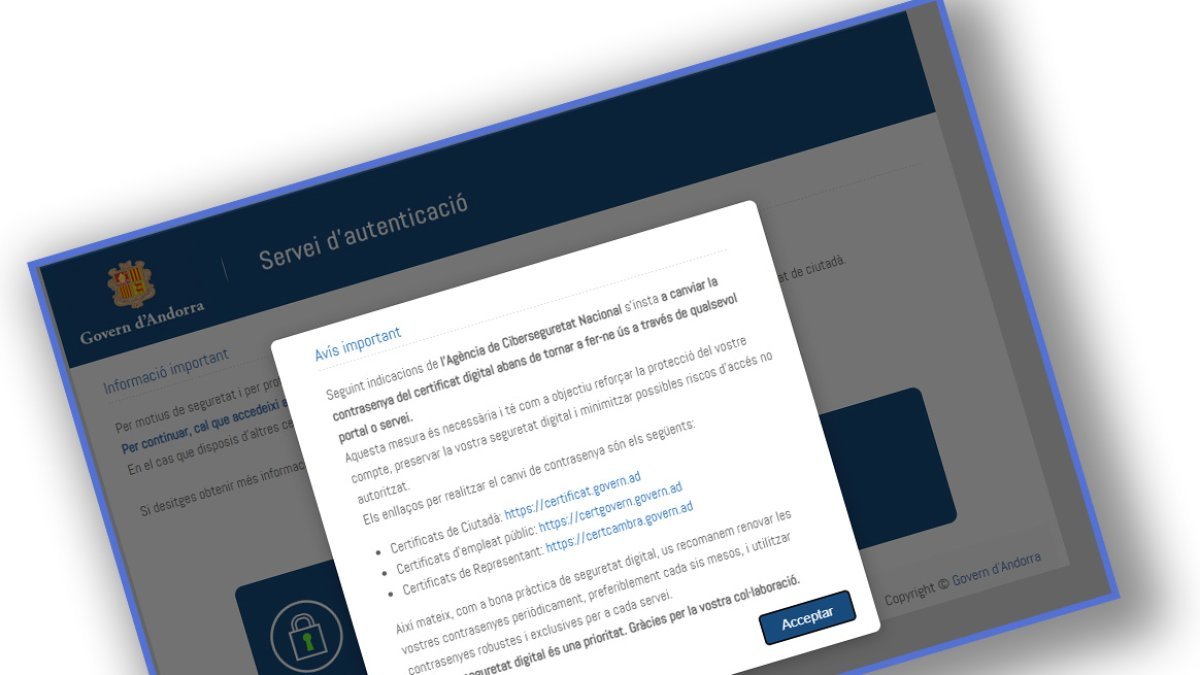
The holder of Digital Transformation ruled out that it is necessary to change the GIRLbecause it is not a password, but he recommended taking extreme precautions against suspicious emails or calls and never providing access keys, in line with the recommendations of the‘ANC-AD and theAPDA. He also pointed out that an information campaign has been carried out on changing passwords for those who need it.
To questions of Cerni Escalé, Rossell defended that the incident shows the need to strengthen international cooperation and coordination between theANC-AD, the police and Andorra Telecom. He recalled that the agency requires audits and follows up.